Why ANAB-Recognised ISO/IEC 27001 Certification Matters
As organisations increasingly rely on digital systems and handle sensitive information, ISO/IEC 27001 certification is essential for building trust and demonstrating strong information security practices.
However, not all certifications carry the same level of global recognition. Certifications issued under ANSI National Accreditation Board (ANAB) accreditation are highly respected internationally, particularly in North America, making them valuable for organisations working with global clients.
ANAB-recognised ISO 27001 certification helps organisations:
- Strengthen credibility with international clients and partners
- Meet supplier and procurement security requirements
- Demonstrate robust, independently verified information security practices
- Improve competitiveness when bidding for global contracts
To support organisations seeking globally recognised certification, Global Compliance Certification (GCC) now offers ISO 27001 certification under ANAB accreditation, enabling clients to achieve internationally trusted certification with the support of GCC’s experienced auditors and efficient, client-focused audit process.
Strengthening Cyber Resilience with Essential Eight (E8MM)
As cyber threats grow in frequency and sophistication, organisations across Australia are increasingly adopting the Australian Signals Directorate (ASD) Essential Eight framework as a practical baseline for cybersecurity.
The Essential Eight consists of eight high-impact security strategies designed to protect against common threats such as malware, ransomware, and credential compromise. Implementing the framework helps organisations:
- Reduce exposure to common cyber attacks
- Demonstrate stronger cybersecurity governance
- Meet government and supply-chain security expectations
- Improve resilience and recovery from cyber incidents
To support organisations on this journey, GCC now offers Essential Eight Assessment services in Australia. GCC provides maturity assessments, gap analysis, and independent evaluation, enabling organisations to demonstrate credible alignment with this widely recognised cybersecurity framework.

GCC Australia Becomes the Only Australian Member of IQNET
GCC Australia has joined International Certification Network (IQNET), becoming the only Australian certification body in the global network. This milestone enhances GCC’s ability to deliver globally recognised certifications and gives certified organisations access to the IQNET Statement of Recognition, global database listing, and use of the IQNET mark. This also provides GCC access to IQNET’s global network of audit resources.
ReadiNow Receives First Accredited ISO 42001 certificate from GCC
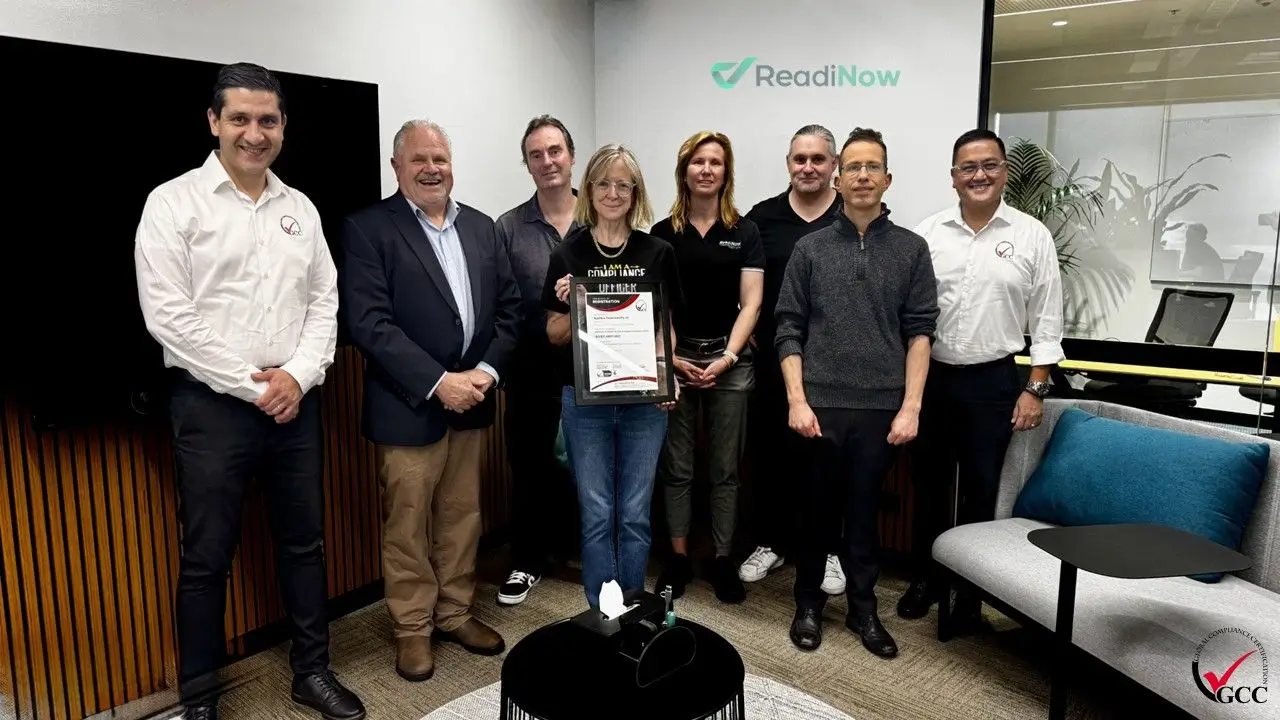
Congratulations to ReadiNow on achieving ISO/IEC 42001 certification for its Artificial Intelligence Management System, demonstrating a strong commitment to responsible AI governance and risk management. This certification also marks an important milestone for Global Compliance Certification (GCC), as it is the first accredited ISO/IEC 42001 certificate issued by GCC following its recent accreditation from JASANZ.

GCC Managing Director Appointed to Standards Australia Committee
We are proud to share that Mousa Sharifi, Managing Director of Global Compliance Certification (GCC), has been elected by members of the Australian Association of Certification Bodies (AACB) to represent them on Standards Australia’s IT-012 Information Security, Cybersecurity and Privacy Protection Committee, supporting Australia’s contribution to standards such as ISO/IEC 27001.
GCC Webinar: Bridging ISOC 27001 with ISO 42001 Governance
Global Compliance Certification (GCC) will host a webinar on ISO/IEC 42001 for AI governance, building on existing ISO/IEC 27001 systems. The session is also ideal for organisations adopting AI or exploring ISO/IEC 42001 certification. GCC will share practical insights and certification tips.
Date & Time: 7 May 2026
Location: Online
How to Prepare for an Information Security Certification

Organisations seeking to achieve ISO 27001 certification or SOC 2 compliance typically follow a structured process designed to assess, strengthen, and validate their information security practices. Certification bodies support this journey by providing independent assessments aligned with recognised international standards, helping organisations demonstrate that appropriate controls are in place.
The key services involved in this process generally include:
1. Gap Analysis and Readiness Assessments
A detailed review of current practices against the requirements of ISO 27001 or SOC 2 helps identify areas of non-conformance or weakness. This process provides organisations with a clear, prioritised roadmap to achieve certification or reporting readiness.
2. Tailored Audit Approach
Audit activities are adapted to reflect the organisation’s size, complexity, industry, and risk profile. This ensures that assessments remain relevant, proportionate, and aligned with the organisation’s operational environment.
3. Independent Audit and Expert Insight
Qualified auditors conduct formal assessments of controls and processes, providing an objective evaluation against the applicable standard. In doing so, they may also highlight practical observations and industry best practices to support continual improvement.
4. Training and Awareness
Training programs help organisations build internal capability by improving staff understanding of information security principles, standard requirements, and their roles in maintaining compliance. This supports more effective implementation and ongoing management of security controls.
5. Certification and Assurance Outcomes
Successful completion of the audit process results in certification (for ISO standards) or an assurance report (for SOC 2). These outcomes provide confidence to clients, regulators, and stakeholders that the organisation’s information security controls have been independently verified.
Together, these services form a structured pathway that enables organisations to strengthen their security posture while demonstrating compliance with internationally recognised frameworks.
How GCC Can Support Your Organisation
Global Compliance Certification (GCC) provides a comprehensive suite of services aligned with the approach outlined above. This includes conducting gap analyses and readiness assessments, delivering independent ISO 27001 certification and SOC 2 examinations, and offering practical, audit-driven insights to support continual improvement.
In addition, GCC delivers targeted training and awareness programs to help organisations build internal capability and better understand their compliance obligations. With experience across a wide range of industries and information security frameworks, GCC supports organisations in navigating the certification journey in a structured, efficient, and internationally recognised manner.